03 / Research notebook
Questions worth testing carefully.
Experiments, limitations, and sourced lab write-ups. Articles are in Vietnamese with English abstracts.
2 articles
RESEARCH · Personal lab evidence
SQL injection: testing the boundary between data and code
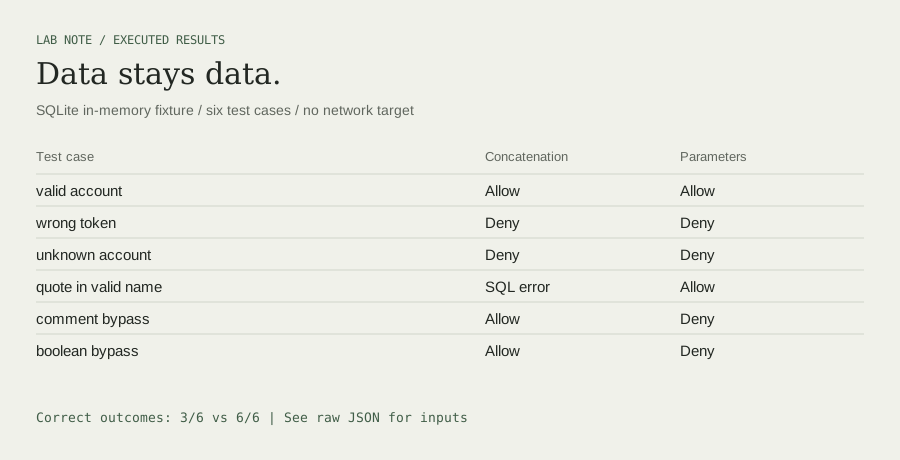
This controlled experiment compares string concatenation and parameter binding in Python’s SQLite interface. Six fixtures cover normal authentication decisions, a legitimate quoted username, and two injection inputs. Both implementations query the same in-memory database. Concatenation produces three correct outcomes, one syntax error, and two authentication bypasses; parameter binding produces all six expected outcomes. These observations illustrate a code–data boundary, not a general security benchmark. The complete input set, executable source, runtime versions, and raw output are provided for reproduction.
15 Sep 2026 · 5 min read →WRITEUP · Reference walkthrough
Appointment: understanding SQL injection authentication bypass
This reference walkthrough examines authentication bypass in Hack The Box's Appointment machine. It connects a small, controlled login test to the underlying SQL parsing error, then proposes evidence collection and regression checks. The emphasis is on explaining why an input changes query logic and what would establish a successful fix. The SQL statement is a teaching model, not recovered application source. No live HTB session was executed for this article, and no personal completion or flag is claimed.
15 Sep 2026 · 4 min read →Personal lab evidence has a local run or log. Reference walkthroughs are sourced learning notes and do not claim machine completion.